I am not going to defend the unacceptable external costs of LLMs here, namely the environmental destruction and the large-scale rug pull on social contracts for creative people.
But adressing your argument, it is totally possible to rewrite the Claude slop to clean, easy to review software. I guess this would be far less work than to reverse-engineer a driver just from captured USB communication.
(That is just my $0.05, but I think the main problem with AI slop in smaller software is not that the code they generate is completely unreadable, but that the LLM systems tend to break down after a few thousand lines, and that they produce architecturally unsound and often subtly wrong software, which leads to an exponentially increasing amount of technical debt if not continously corrrected by experienced people.)
Good luck finding a malware repository for undocumented proprietary hardware
Reverse engineering is actually a very good use case for LLMs. Its like using a black box to get a different black box to do a trick. It might not be epistemologically sound, but if it can boot the kernel, who cares?


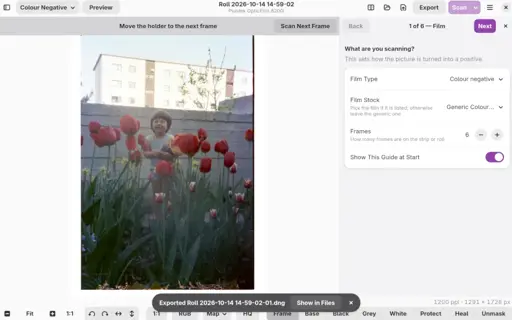
If I wanted a virus on my device, I’ll just go to a malware repository rather than trust low quality slopware.
I am not going to defend the unacceptable external costs of LLMs here, namely the environmental destruction and the large-scale rug pull on social contracts for creative people.
But adressing your argument, it is totally possible to rewrite the Claude slop to clean, easy to review software. I guess this would be far less work than to reverse-engineer a driver just from captured USB communication.
(That is just my $0.05, but I think the main problem with AI slop in smaller software is not that the code they generate is completely unreadable, but that the LLM systems tend to break down after a few thousand lines, and that they produce architecturally unsound and often subtly wrong software, which leads to an exponentially increasing amount of technical debt if not continously corrrected by experienced people.)
Good luck finding a malware repository for undocumented proprietary hardware
Reverse engineering is actually a very good use case for LLMs. Its like using a black box to get a different black box to do a trick. It might not be epistemologically sound, but if it can boot the kernel, who cares?